Talk to an Expert

Windows Kernel Exploitation Framework

KEF is a Windows kernel offensive tool built by WebSec for red teams, government agencies, law enforcement, military cyber units, and vetted operators. The platform provides kernel-mode access to evaluate EDR and XDR defenses, test detection pipelines, and run realistic adversary simulations across hardened Windows deployments.

decorative

What is the Kernel Exploitation Framework?

The Kernel Exploitation Framework (KEF) is an offensive security platform built by WebSec for in-depth Windows security testing. Operators gain direct kernel-level visibility and precise control over processes, access tokens, protection levels, callbacks, ETW providers, WFP callouts, minifilters, and related security mechanisms.

Standard offensive security utilities run in user mode, where host defenses easily monitor or block them. KEF operates directly in Windows kernel mode at ring0, sharing the same operating system privilege domain as the Windows kernel, drivers, and modern EDR, XDR, antivirus, and endpoint-monitoring sensors.

WebSec developed KEF for authorized red teams, government agencies, law enforcement, military cyber units, intelligence operators, vulnerability researchers, and control validation teams. It runs reliably in hardened Windows environments where conventional user-mode tools are restricted, detected, or blocked outright.

Benefits of the WebSec Kernel Exploitation Framework

Kernel-Level Security Testing - Test hardened Windows targets from ring0 to validate defenses that user-mode security utilities cannot adequately evaluate.
Realistic Adversary Simulation - Emulate sophisticated attack techniques to test EDR, XDR, SIEM pipelines, endpoint hardening rules, and SOC response teams.
Centralized Operator Control - Control processes, tokens, callbacks, telemetry providers, WFP callouts, and protection levels from one consolidated console.
Detection Engineering Support - Match timestamped operator actions against endpoint and SIEM logs to uncover blind spots and refine defensive alerting.

Advanced Windows Kernel Security Testing

Modern endpoint security suites enforce their core protections inside the Windows kernel. Because KEF operates within this same ring0 domain, operators have the direct visibility and control needed to evaluate active kernel callbacks, process protections, access tokens, ETW telemetry feeds, WFP callouts, filesystem minifilters, and OS security hooks.

Instant Ring0 Access

Acquire controlled ring0 execution from guest or unprivileged user sessions, then verify direct escalation paths to SYSTEM during authorized security assessments on hardened Windows endpoints.

Low-Noise Initial Access

KEF deploys through a low-noise execution flow that lets red team operators enter systems cleanly while testing active endpoint sensors and SOC monitoring rules.

Advanced Kernel Operations

Execute an extensive range of kernel tasks spanning process control, token editing, callback handling, telemetry auditing, DLL injection, and defense-mechanism testing through a single unified operator interface.

KEF Hardware Access Device

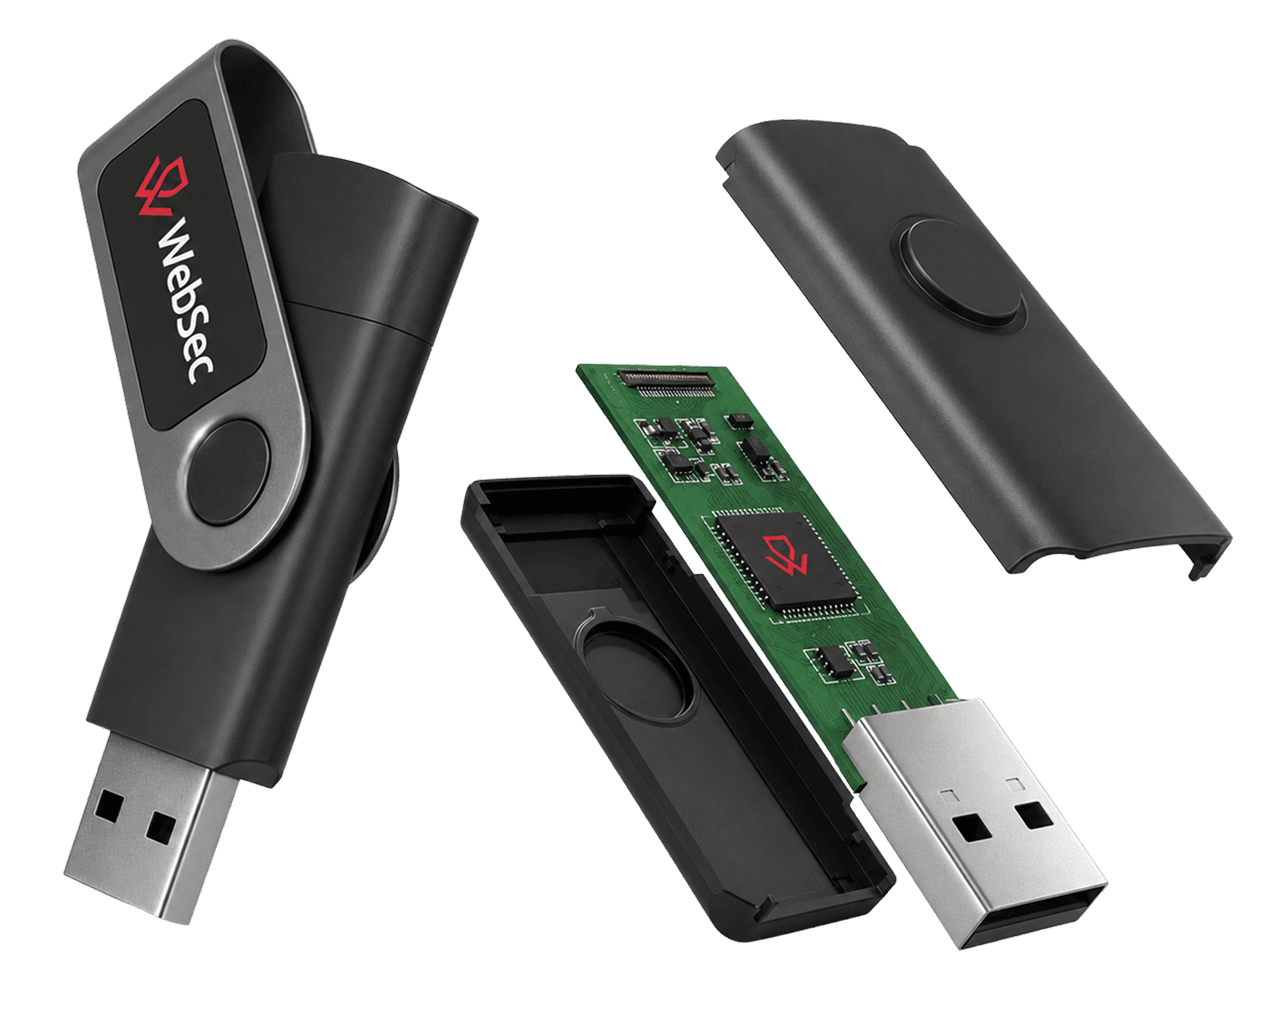
The portable KEF hardware device gives operators a secure, controlled method to deploy and use the Kernel Exploitation Framework across supported Windows endpoints.

Customer-Controlled Activation

The device stays locked until unlocked with a key generated from the KEF Client Web Interface. Every generated key unlocks the hardware for an operational window of up to 24 hours.

Rapid Deployment

Operators can connect and initialize the framework quickly during assessments or active red team operations without dealing with lengthy setup procedures.

Built for Hardened Environments

Built to operate reliably on locked-down Windows systems where standard user-mode tools encounter execution blocks, policy limits, or EDR alerts.

Modern Windows Compatibility

Runs on contemporary Windows workstations and servers, with verified support for Windows 10, Windows 11, and current Windows Server releases.

Software Demo

<p>Operators can inspect kernel callbacks, ETW providers, WFP callouts, process tokens, and active security states through either the desktop GUI or the terminal TUI/CLI.</p>

How the Kernel Exploitation Framework Works

Three steps from controlled activation to advanced Windows kernel security testing

Step #1

Activate

Plug in the KEF hardware device and enter an activation key generated through the KEF Client Web Interface. Each validated key unlocks an authorized operational window lasting up to 24 hours.
Step #2

Initialize

KEF establishes ring0 kernel access, loads its core driver components, and readies the framework for testing on the target system.
Step #3

Operate

Use either the GUI or TUI to run authorized modules, execute targeted operations, review live outputs, and log every operator action for detection engineering and reporting.

Why Red Teams Choose KEF

Native Windows Kernel-Level Testing

Standard offensive security tools run in user mode, where endpoint agents can easily monitor, intercept, or kill them. KEF runs directly in kernel mode at ring0, working alongside the callbacks, telemetry providers, and enforcement filters that Windows and top-tier EDR or XDR products use to protect systems.

Precise and Controlled Operations

Operators can manipulate individual processes, callbacks, ETW providers, callouts, and minifilters with precision, avoiding clumsy system crashes or unneeded operational noise.

Developed by Offensive Security Specialists

WebSec researchers and red team operators built KEF around Windows internals expertise. Every module reflects hands-on tradecraft developed during offensive simulations, exploit analysis, and defensive validation exercises.

Full Operator Logging

KEF logs operator commands alongside accurate timestamps. Red teams and detection engineers can match unalerted actions against exact runtime events and build reliable detections for what slipped through.

Who Can Use the Kernel Exploitation Framework?

KEF is a restricted offensive security utility available exclusively to vetted organizations that operate under a legal mandate and an approved operational scope.

Government Security Agencies

National security missions, critical infrastructure audits, and controlled resilience testing against hardened Windows infrastructure.

Military Cyber Units

Tactical system access, advanced cyber operations, internal research, and defensive readiness assessments across authorized testing environments.

Law Enforcement

Legally mandated technical operations needing reliable ring0 access, process inspection capabilities, and audited operator activity.

Red Team Operators

Realistic adversary emulation to evaluate EDR and XDR products, audit endpoint hardening policies, and challenge incident response team readiness.

Intelligence Teams

Specialized technical intelligence assignments that depend on deep Windows visibility and fine-grained kernel-mode interaction.

Windows Kernel Exploitation Framework Features

Six core capability areas for advanced Windows offensive security testing

Kernel Callback Manager

Enumerate, inspect, selectively remove, and restore active kernel callbacks and minifilters monitoring process execution, thread creation, image loading, registry changes, object access, and filesystem activity.

Security Control Testing

Test defensive resilience by assessing ETW TI, Core Isolation, HVCI, user-mode hooks, minifilters, and chosen kernel callbacks through targeted or automated batch operations.

WFP Callout Inspector

Enumerate, review, mute, and restore Windows Filtering Platform callouts while viewing parent driver details, entry point addresses, run state, and active network filter rules.

ETW Provider Control

Find, analyze, disable, and restore Event Tracing for Windows providers, showing exactly which EDR, XDR, antivirus, or OS services subscribe to their telemetry streams.

Process and Token Control

Examine target processes, adjust access tokens, swap tokens, grant privileges, modify integrity and PPL levels, kill stubborn processes, and manage process execution safely.

Ring0 Privilege Escalation

Establish immediate Windows kernel-mode capabilities from guest or unprivileged user accounts and validate direct escalation to SYSTEM without relying on public exploits or vulnerable third-party drivers.

Windows Kernel Exploitation Framework FAQ's

decorative image about frequently asked questions

Ready to Work with Websec? Inquire Now

Ready to elevate your cybersecurity with WebSec? Take the first step towards fortified protection. Inquire now and secure your digital assets with our trusted expertise.
Personal info